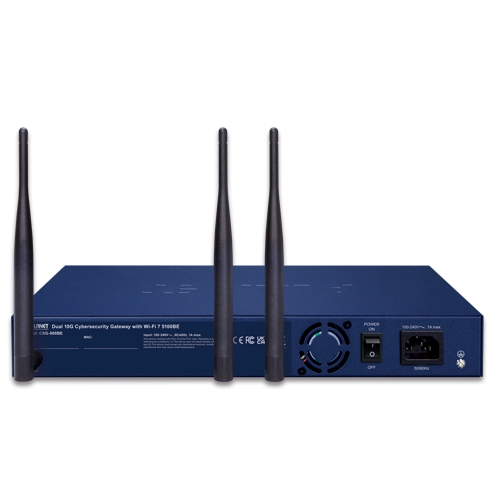
بيانات المنتج

  • rank_math_internal_links_processed: 1
  • إجمالي المبيعات: 0
  • رمز المنتج: PQCG-800BE
  • علامة تبويب التطبيقات: <p><strong>Post-Quantum Protection for Critical Enterprise Networks</strong><p>ال <strong>PQCG-800BE</strong> provides secure connectivity for government agencies, financial institutions, and enterprise networks handling sensitive information. <strong>Hybrid PQC TLS</strong> supports long-term communication security, while<strong> PUF-based configuration protection</strong> allows only paired devices with an inserted <strong>CoreTrust Key</strong> to modify gateway settings. Devices that do not meet both requirements cannot change settings even after login. Integrated <strong>IDS/IPS</strong>, <strong>Layer 7 DPI</strong>, <strong>security logs</strong>, <strong>and scheduled signature updates</strong> help administrators detect threats and monitor security events across headquarters, branch offices, and remote sites.</p><p> </p><p><img style="display: block; margin-left: auto; margin-right: auto;" src="https://www.planet.com.sa/wp-content/uploads/2026/10/PQCG-800-3.png" alt="" width="700" height="323"></p><p> </p><p><strong>Secure Wi-Fi 7 Connectivity with Centralized Network Management</strong></p><p>ال <strong>PQCG-800BE</strong> combines <strong>Wi-Fi 7 5100BE dual-band connectivity</strong> with enterprise cybersecurity and centralized network management for business offices and branch networks. With a built-in <strong>وحدة تحكم نقاط الوصول</strong>,<strong> بوابة الوصول المقيد</strong>,<strong> مصادقة RADIUS</strong>, <strong>and DHCP server</strong>, administrators can centrally manage wireless APs and deploy employee and guest networks with separate access policies. Integrated <strong>IDS/IPS</strong>, <strong>Layer 7 DPI</strong>, <strong>and firewall protection</strong> help safeguard wired and wireless traffic, while <strong>dual 10G WAN interfaces</strong>, <strong>SD-WAN</strong>, <strong>and automatic failover</strong> provide reliable connectivity for cloud applications and daily business operations.</p><p> </p><p><img style="display: block; margin-left: auto; margin-right: auto;" src="https://www.planet.com.sa/wp-content/uploads/2026/10/PQCG-800BE-1.png" alt="" width="700" height="475"></p></p>
  • key_features_tab: <p><strong>أبرز النقاط</strong><ul> <li><strong>PUF-based configuration protection requiring completed device pairing and an inserted CoreTrust Key</strong></li> <li><strong>Hybrid Post-Quantum TLS</strong> for long-term protection against quantum-computing threats</li> <li>Anti-SCA protection to help safeguard cryptographic keys</li> <li>Trusted platform security with Secure Boot and PUF-assisted hardware TRNG</li> <li>Advanced threat protection with IDS/IPS, Layer 7 DPI, content filtering and application visibility</li> <li>Zero Trust and identity-based access with FIDO2 Passkey, TOTP MFA, certificate authentication and ZTNA</li> <li>شبكة VPN متعددة البروتوكولات مع IPSec و OpenVPN و WireGuard و GRE و PPTP و L2TP</li> <li>واجهات WAN مزدوجة بسرعة 10 جيجابت مع تقنية SD-WAN، وموازنة الأحمال، والتحويل التلقائي في حالة الفشل، والتوافر العالي</li> <li><strong>Wi-Fi 7 5100BE</strong> dual-band wireless connectivity with up to 5100Mbps</li> <li>وحدة تحكم نقاط الوصول المتكاملة، وبوابة الوصول المقيدة، وRADIUS، ونظام إدارة الشبكة السحابية (CloudNMS)، ومراقبة الأمان</li> </ul><p> </p><p><strong>الأجهزة</strong></p><ul> <li>4 منافذ RJ45 من نوع 10/100/1000BASE-T</li> <li>1 1G/2.5G/5G/10GBASE-T RJ45 port for WAN/LAN interface</li> <li>فتحة SFP+ واحدة بسرعة 1 جيجابت/2.5 جيجابت/10 جيجابت إيثرنت لواجهة WAN/LAN</li> <li>منفذ USB واحد لعمل نسخ احتياطية واستعادة إعدادات النظام</li> <li>Reset button</li> <li>تركيب على سطح المكتب أو تركيب على رف</li> </ul><p> </p><p><strong>واجهة واي فاي 7 اللاسلكية</strong></p><ul> <li>Supports Wi-Fi 7 (802.11be) dual-band wireless connectivity</li> <li>Provides combined wireless speeds of up to 5100Mbps, with approximately 689Mbps at 2.4GHz and 4324Mbps at 5GHz</li> <li>Supports up to 160MHz channel bandwidth</li> <li>Supports 4096-QAM (4K-QAM) for increased wireless throughput</li> <li>Advanced MIMO technology for high-performance wireless connectivity</li> <li>Dual-band 2.4GHz and 5GHz operation for flexible wireless deployment</li> </ul><p> </p><p><strong>أمان المنصة الموثوقة</strong></p><ul> <li><strong>PUF-based configuration change authorization requiring completed device pairing and an inserted CoreTrust Key</strong></li> <li><strong>Prevents configuration changes when either requirement is not met, even after connecting and logging in</strong></li> <li>التمهيد الآمن لضمان تشغيل البرامج الثابتة الموثوقة والمصادق عليها فقط أثناء بدء تشغيل النظام</li> <li>PUF-assisted hardware TRNG (True Random Number Generator) for secure cryptographic key generation</li> <li>Anti-Side-Channel Attack (Anti-SCA) protection to help safeguard cryptographic keys</li> <li>يتبع تصميم الأمن مبادئ قانون المرونة السيبرانية للاتحاد الأوروبي (CRA).</li> </ul><p> </p><p><strong>جدار الحماية والتحكم المروري</strong></p><ul> <li>جدار الحماية الخاص بفحص الحزم ذي الحالة (SPI)</li> <li>MAC filtering and IP filtering</li> <li>بوابات طبقة التطبيق (NAT ALGs)</li> <li>دعم إعادة توجيه المنافذ ومنطقة DMZ</li> </ul><p> </p><p><strong>Advanced Threat Protection & Application Security</strong></p><ul> <li>Intrusion Detection and Prevention (IDS/IPS)</li> <li>Layer 7 Deep Packet Inspection (DPI)</li> <li>Application-level traffic visibility</li> <li>Content filtering</li> <li>DoS/DDoS mitigation</li> <li>SYN/ICMP flooding protection</li> <li>Automatic and scheduled threat signature updates</li> </ul><p> </p><p><strong>Zero Trust & ZTNA</strong></p><ul> <li>Zero Trust access control</li> <li>Identity-based access policy</li> <li>Built-in ZTNA for secure application-level access</li> <li>Zero Trust-protected VPN access</li> <li>Identity-based VPN authentication</li> </ul><p> </p><p><strong>Identity, Authentication & Access Services</strong></p><ul> <li>FIDO2 Passkey authentication</li> <li>TOTP-based multi-factor authentication (MFA/2FA)</li> <li>Certificate-based authentication</li> <li>خادم/عميل RADIUS</li> <li>Captive Portal for controlled employee and guest access</li> </ul><p> </p><p><strong>شبكة VPN ونفق آمن</strong></p><ul> <li>IPSec/خادم بعيد (من الشبكة إلى الشبكة، ومن المضيف إلى الشبكة)</li> <li>خادم GRE، خادم PPTP</li> <li>خادم L2TP</li> <li>خادم/عميل SSL (OpenVPN، متوافق مع خدمات VPN مثل Surfshark و NordVPN)</li> <li>خادم/عميل WireGuard</li> <li>طرق التشفير: DES، 3DES، AES، AES-128/192/256</li> <li>طرق المصادقة: MD5، SHA-1، SHA-256، SHA-384، SHA-512</li> <li>Supports up to 100 concurrent SSL VPN connections*</li> </ul><p> </p><p><strong>التشفير والاستعداد الكمي</strong></p><ul> <li><strong>Hybrid Post-Quantum TLS key exchange using ML-KEM (Kyber) for protection against future quantum-computing threats</strong></li> </ul><p> </p><p><strong>التوجيه، وشبكات SD-WAN، وتحسين شبكات WAN</strong></p><ul> <li>المسار الثابت</li> <li>Dynamic route</li> <li>بروتوكول OSPF</li> <li>تقنية SD-WAN لتحسين حركة البيانات عبر شبكات WAN المتعددة</li> <li>موازنة الأحمال الصادرة</li> <li>تعطيل دعم NAT لنشر وضع التوجيه النقي</li> </ul><p> </p><p><strong>التوافر العالي ومرونة الشبكة الواسعة</strong></p><ul> <li>Automatic failover for dual WAN</li> <li>التوافر العالي (HA)</li> </ul><p> </p><p><strong>خدمات الشبكة</strong></p><ul> <li>عميل IP ثابت/PPPoE/DHCP لشبكة WAN</li> <li>خادم DHCP وعميل NTP للشبكة المحلية</li> <li>البروتوكولات: TCP/IP، UDP، ARP، IPv4، IPv6</li> <li>جودة الخدمة، وبروتوكول إدارة مجموعات الإنترنت، وبروتوكول نقطة الاتصال الموحدة</li> <li>استنساخ عنوان MAC</li> <li>خدمة DDNS: PLANET DDNS، وEasy DDNS، وDynDNS، وNo-IP</li> </ul><p> </p><p><strong>إدارة الشبكات اللاسلكية ونقاط الوصول</strong></p><ul> <li>وحدة تحكم مدمجة لإدارة نقاط الوصول الذكية من PLANET بشكل مركزي</li> <li>توفير مركزي لـ SSID والراديو وسياسة الأمان</li> <li>توفير نقاط الوصول بكميات كبيرة وترقية البرامج الثابتة</li> </ul><p> </p><p><strong>إدارة النظام ومراقبته وإعداد التقارير</strong></p><ul> <li>معالج الإعداد</li> <li>لوحة تحكم لمراقبة النظام والأمان</li> <li>عارض سجلات الأمان وتقارير الأحداث</li> <li>جهاز مراقبة التشخيص الرقمي (SFP-DDM)</li> <li>إمكانية الوصول الآمن للإدارة عبر بروتوكول HTTPS؛ يدعم الوصول عبر بروتوكول HTTP</li> <li>إدارة SNMPv1 و SNMPv2c و SNMPv3</li> <li>إعادة التشغيل التلقائي</li> <li>نظام إدارة الشبكة PLANET وأداة الاكتشاف الذكي لإدارة النشر</li> <li>تطبيق PLANET CloudNMS للمراقبة في الوقت الفعلي</li> </ul></p>
  • علامة تبويب المواصفات: <table style="width:100%;" class="common_table_sky"><thead><tr><th colspan="2">مواصفات الأجهزة</th></tr></thead><tbody><tr><td class="align-middle">إيثرنت</td><td>4 منافذ إيثرنت RJ45 من نوع 10/100/1000BASE-T (من المنفذ 1 إلى المنفذ 4)<br /> 1 منفذ RJ45 بسرعة 1 جيجابت/2.5 جيجابت/5 جيجابت/10 جيجابت (المنفذ 5)<br /> <small><em>يدعم وضع منفذ WAN أو وضع منفذ LAN عبر تكوين البرنامج</em></small></td></tr><tr><td class="align-middle">الفيبر</td><td>منفذ واحد من نوع SFP+ بسرعة 1 جيجابت/2.5 جيجابت/10 جيجابت إيثرنت (المنفذ 6)<br /> <small><em>يدعم وضع منفذ WAN أو وضع منفذ LAN عبر تكوين البرنامج</em></small></td></tr><tr><td class="align-middle">منفذ USB</td><td>منفذ USB 2.0 واحد لعمل نسخ احتياطية واستعادة إعدادات النظام</td></tr><tr><td class="align-middle">زر إعادة الضبط</td><td>إعادة ضبط المصنع الافتراضي</td></tr><tr><td class="align-middle">مروحة حرارية</td><td>1</td></tr><tr><td class="align-middle">مؤشرات LED</td><td>نظام:<br />  PWR, Internet, (<font color="Green">أخضر</font>)<br /> واجهات لاسلكية (2.4 جيجا هرتز و 5 جيجا هرتز)<br /> LNK/ACT (<font color="Green">أخضر</font>)<br /> واجهات إيثرنت (المنافذ من 1 إلى 4):<br /> 10/100/1000 LNK/ACT (<font color="Green">أخضر</font>)<br /> واجهات إيثرنت (المنفذ 5):<br /> 1G/2.5G/5G/10G LNK/ACT (<font color="Green">أخضر</font>)<br /> واجهات الألياف (المنفذ 6):<br /> 1G/2.5G/10G LNK/ACT (<font color="Green">أخضر</font>)</td></tr><tr><td class="align-middle">تثبيت</td><td>تركيب على سطح المكتب أو تركيب على رف</td></tr><tr><td class="align-middle">متطلبات الطاقة</td><td>100-240 فولت تيار متردد، 50/60 هرتز، استشعار تلقائي</td></tr><tr><td class="align-middle">استهلاك الطاقة / تبديدها</td><td>Max. 3.3 watts/10.92BTU (Power on without any connection)<br /> Max. 11 watts/37.53BTU (Full loading)</td></tr><tr><td class="align-middle">وزن</td><td>1725 غرام</td></tr><tr><td class="align-middle">الأبعاد (العرض × العمق × الارتفاع)</td><td>330.2 × 200 × 43.1 مم، ارتفاع وحدة واحدة</td></tr><tr><td class="align-middle">حاوية</td><td>معدن</td></tr></tbody><thead><tr><th colspan="2">مواصفات الاتصال اللاسلكي</th></tr></thead><tbody><tr><td class="align-middle">معيار لاسلكي</td><td>IEEE 802.11be (Wi-Fi 7)</td></tr><tr><td class="align-middle">نطاق التردد</td><td>2.4 جيجاهرتز و 5 جيجاهرتز</td></tr><tr><td class="align-middle">معدل نقل البيانات اللاسلكية</td><td>سرعة تصل إلى 5100 ميجابت في الثانية</td></tr><tr><td class="align-middle">معدل نقل البيانات 2.4 جيجاهرتز</td><td>تصل السرعة إلى حوالي 689 ميجابت في الثانية</td></tr><tr><td class="align-middle">معدل نقل البيانات 5 جيجاهرتز</td><td>تصل إلى حوالي 4324 ميجابت في الثانية</td></tr><tr><td class="align-middle">عرض القناة</td><td>يصل إلى 160 ميجاهرتز</td></tr><tr><td class="align-middle">تعديل</td><td>4096-QAM (4K-QAM)</td></tr><tr><td class="align-middle">MIMO</td><td>تقنية MIMO المتقدمة</td></tr></tbody><thead><tr><th colspan="2">خدمات الأمن</th></tr></thead><tbody><tr><td class="align-middle">Hardware Root of Trust</td><td>PUF-based hardware protection for configuration change authorization</td></tr><tr><td class="align-middle">Configuration Change Authorization</td><td>Requires completed device pairing and an inserted CoreTrust Key to modify gateway settings.<br /> Devices without either requirement cannot change settings, even after connecting and logging in.</td></tr><tr><td class="align-middle">Side-Channel Attack Protection</td><td>Anti-SCA protection to help safeguard cryptographic keys against side-channel attacks</td></tr><tr><td class="align-middle">Hardware Random Number Generator</td><td>PUF-assisted hardware TRNG for secure cryptographic key generation</td></tr><tr><td class="align-middle">أمان جدار الحماية</td><td>Hardware TRNG for secure cryptographic key generation<br /> فحص الحزم ذي الحالة (SPI)<br /> Security log and event reporting<br /> Automatic threat signature updates<br /> يحجب هجمات حجب الخدمة/هجمات حجب الخدمة الموزعة<br /> Role-based access policy enforcement</td></tr><tr><td class="align-middle">ALG (بوابة طبقة التطبيق)</td><td>SIP، RTSP، FTP، H.323، TFTP</td></tr><tr><td class="align-middle">NAT</td><td>نقل البضائع<br /> مضيف منطقة منزوعة السلاح<br /> UPnP<br /> تعطيل NAT (يدعم وضع التوجيه)</td></tr><tr><td class="align-middle">تصفية المحتوى</td><td>تصفية عناوين MAC<br /> تصفية عناوين IP<br /> تصفية الويب</td></tr><tr><td class="align-middle">إدارة عرض النطاق الترددي</td><td>موازنة الأحمال الصادرة<br /> تجاوز الأعطال لشبكة WAN المزدوجة<br /> جودة الخدمة (QoS)</td></tr><tr><td class="align-middle">Zero Trust</td><td>Zero Trust access control with identity verification<br /> Multi-factor authentication via external hardware security key support</td></tr><tr><td class="align-middle">Intrusion Prevention System</td><td>Intrusion Detection and Prevention (IDS/IPS)<br /> Layer 7 Deep Packet Inspection (DPI)<br /> Application-level traffic visibility</td></tr><tr><td class="align-middle">نظام تثبيت آمن</td><td>Establishes a <b>Chain of Trust (CoT)</b> across all boot stages via cryptographic image signature verification</td></tr></tbody><thead><tr><th colspan="2">التواصل</th></tr></thead><tbody><tr><td class="align-middle">وضع التشغيل</td><td>وضع التوجيه</td></tr><tr><td class="align-middle">بروتوكول التوجيه</td><td>المسار الثابت، المسار الديناميكي (RIP)، بروتوكول OSPF</td></tr><tr><td class="align-middle">شبكة VLAN</td><td>802.1Q Tag-based, Port-based, Multi-VLAN</td></tr><tr><td class="align-middle">البث المتعدد</td><td>وكيل IGMP</td></tr><tr><td class="align-middle">معدل نقل البيانات عبر NAT</td><td>Max. 9.4Gbps</td></tr><tr><td class="align-middle">موازنة الأحمال الصادرة</td><td>الخوارزميات المدعومة: الوزن</td></tr><tr><td class="align-middle">بروتوكول</td><td>IPv4، IPv6، TCP/IP، UDP، ARP، HTTP، HTTPS، NTP، DNS، PLANET DDNS، PLANET Easy DDNS، DHCP، PPPoE، SNMPv1/v2c/v3</td></tr><tr><td class="align-middle">الميزات الرئيسية</td><td>HA (التوافر العالي)<br /> بوابة الوصول المقيد<br /> خادم/عميل RADIUS<br /> التحكم في نقاط الوصول</td></tr></tbody><thead><tr><th colspan="2">VPN</th></tr></thead><tbody><tr><td class="align-middle">وظيفة VPN</td><td>IPSec (Net-to-Net, Host-to-Net)<br /> IPSec Remote Server<br /> اختبار GRE<br /> خادم PPTP<br /> خادم L2TP<br /> SSL Server<br /> SSL Client (Open VPN, Surfshark, NordVPN, PureVPN)<br /> WireGuard VPN Server/Client</td></tr><tr><td class="align-middle">سعة نفق VPN حسب البروتوكول</td><td>IPSec: 16<br /> GRE: 5<br /> PPT: 100<br /> SSL VPN: 200</td></tr><tr><td class="align-middle">معدل نقل بيانات VPN</td><td>L2TP (1Gbps): 145~463Mbps<br /> L2TP (10Gbps): 483~885Mbps<br /> L2TP/IPsec (1Gbps): 150~334Mbps<br /> L2TP/IPsec (10Gbps): 438~496Mbps<br /> IPsec/AES128 (1Gbps): 894~910Mbps<br /> IPsec/AES128 (10Gbps): 1,110~1,310Mbps<br /> IPsec/AES256 (1Gbps): 752~842Mbps<br /> IPsec/AES256 (10Gbps): 864~1,060Mbps<br /> WireGuard (1Gbps): 815~883Mbps<br /> WireGuard (10Gbps): 1,430~1,890Mbps</td></tr><tr><td class="align-middle">أساليب التشفير</td><td>تشفير DES أو 3DES أو AES أو AES-128/192/256<br /> بروتوكول PQC TLS (بروتوكول أمان طبقة النقل بعد التشفير الكمي) جاهز<br /> Supports Hybrid Post-Quantum TLS key exchange using ML-KEM (Kyber)</td></tr><tr><td class="align-middle">أساليب المصادقة</td><td>SHA-256/SHA-384/SHA-512 authentication algorithm<br /> TLS_KYBER_RSA_WITH_AES_256_GCM_SHA384<br /> FIDO2 Passkey authentication<br /> Certificate-based authentication<br /> TOTP MFA<br /> مصادقة RADIUS</td></tr></tbody><thead><tr><th colspan="2">إدارة</th></tr></thead><tbody><tr><td class="align-middle">واجهات الإدارة الأساسية</td><td>متصفح الويب<br /> SNMP الإصدار 1، الإصدار 2c<br /> أداة PLANET Smart Discovery / UNI-NMS مدعومة<br /> PLANET NMS System/CloudNMS</td></tr><tr><td class="align-middle">واجهات إدارة آمنة</td><td>SSHv2، TLSv1.3، SNMP v3</td></tr><tr><td class="align-middle">سجل النظام</td><td>سجل أحداث النظام<br /> Security Log<br /> Event Report<br /> Scheduled Signature Update</td></tr><tr><td class="align-middle">آحرون</td><td>معالج الإعداد<br /> لوحة التحكم<br /> حالة النظام/الخدمة<br /> إحصائيات<br /> Security Monitoring Dashboard<br /> حالة الاتصال<br /> إعادة التشغيل التلقائي<br /> التشخيص</td></tr></tbody><thead><tr><th colspan="2">الامتثال للمعايير</th></tr></thead><tbody><tr><td class="align-middle">الامتثال التنظيمي</td><td>CE، FCC</td></tr></tbody><thead><tr><th colspan="2">مواصفات البيئة</th></tr></thead><tbody><tr><td class="align-middle">التشغيل</td><td>درجة الحرارة: من 0 إلى 50 درجة مئوية<br /> الرطوبة النسبية: 5 ~ 95% (بدون تكثف)</td></tr><tr><td class="align-middle">تخزين</td><td>درجة الحرارة: من -10 إلى 60 درجة مئوية<br /> الرطوبة النسبية: 5 ~ 95% (بدون تكثف)</td></tr></tbody></table>
  • عدد مشاهدات منشورات ekit: 16

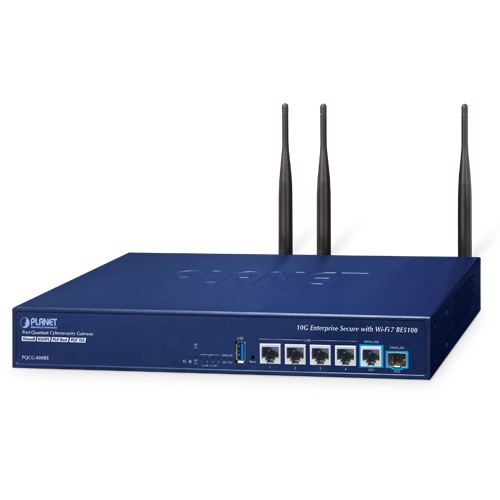
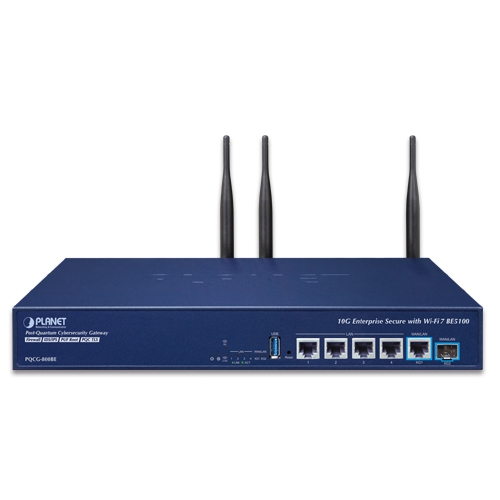
بوابة أمن سيبراني مزدوجة مقاومة للحوسبة الكمومية، تدعم تقنية PUF بسرعة 10 جيجابت/ثانية، مزودة بتقنية Wi-Fi 7 5100BE

» PQCG-800BE

PUF-Anchored Quantum-Resilient Cybersecurity Gateway

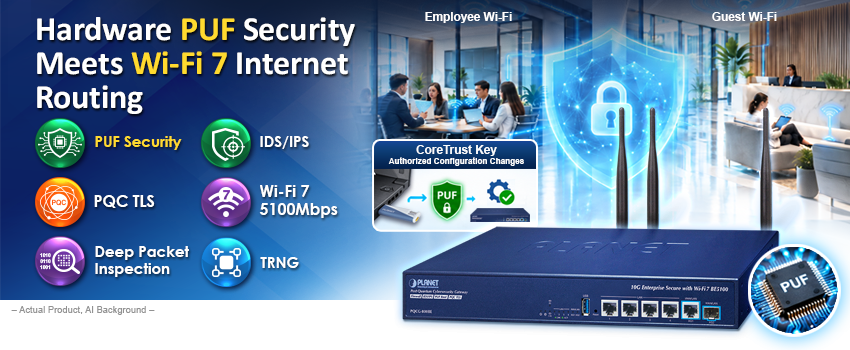
The PLANET PQCG-800BE is an enterprise-grade PUF-Anchored Quantum-Resilient Cybersecurity Gateway built with a PUF-based Hardware Root of Trust to strengthen device security from the hardware level. Combining hardware-rooted protection, post-quantum cryptography, IDS/IPS, Layer 7 DPI, Zero Trust authentication و multi-protocol VPN, the PQCG-800 provides comprehensive protection for enterprise and critical network environments. Its PUF-based security architecture also supports hardware-backed configuration authorization through the PLANET CoreTrust Key, helping prevent unauthorized changes to critical gateway settings even when login credentials are compromised. Powered by a quad-core processor with dual 10G واجهات و Wi-Fi 7 connectivity, it delivers high-performance secure connectivity for demanding network deployments.
 

edm2 PQCG 800BE 

PUF-Based Hardware Root of Trust and Configuration Protection

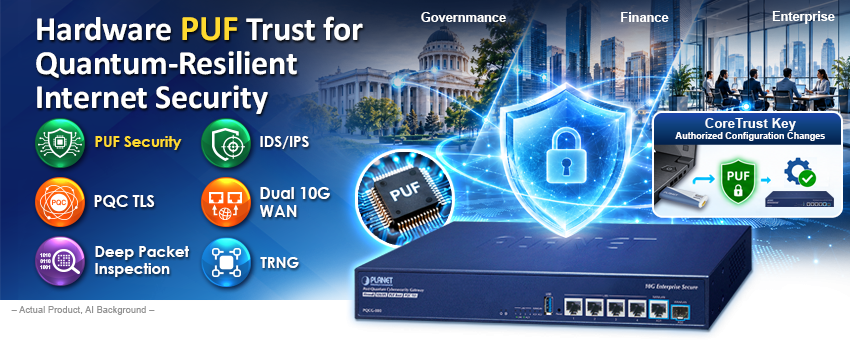
At the core of the PQCG-800BE is Physical Unclonable Function (PUF) technology, which establishes a hardware-rooted trust foundation for protecting security-critical operations. For configuration change authorization, the gateway works with the CoreTrust Key and a paired management device to provide an additional hardware-backed control layer. Only a device that has completed pairing and has the authorized CoreTrust Key inserted can modify protected gateway settings. Even if an unauthorized user gains network access or valid login credentials, configuration changes remain restricted without the required hardware authorization, helping reduce the risk of credential-based takeover and unauthorized security policy modification.
 

edm2 PQCG 800 1


Post-Quantum Cryptography for Long-Term Data Protection

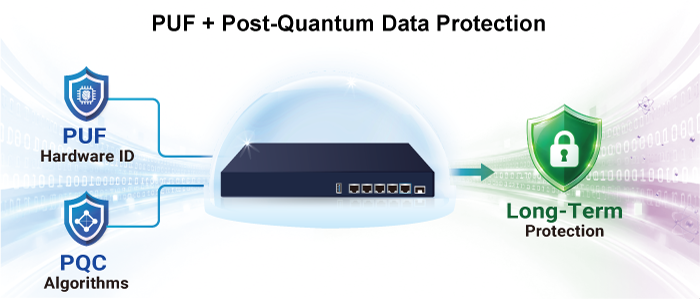
Building on its PUF-based Hardware Root of Trust, the PQCG-800BE incorporates post-quantum cryptographic technologies to strengthen communications against emerging quantum-computing threats. This quantum-resilient security architecture is designed to address risks such as “harvest now, decrypt later”, where encrypted information captured today could potentially be decrypted by future quantum computers. By combining hardware-rooted trust with post-quantum protection, the PQCG-800BE provides a stronger security foundation for long-term protection of sensitive enterprise and critical infrastructure communications.
 

PQCG 800 2


Anti-SCA Protection and PUF-Assisted Hardware TRNG

The PQCG-800BE integrates Anti-Side-Channel Attack (Anti-SCA) protection to help safeguard cryptographic keys against leakage through side-channel attacks. A PUF-assisted Hardware True Random Number Generator (TRNG) supports secure cryptographic key generation, further strengthening the gateway’s hardware security foundation.


Advanced Threat Protection with Built-in IDS/IPS and Layer 7 Deep Packet Inspection

The PQCG-800BE integrates built-in Intrusion Detection and Prevention (IDS/IPS) with Layer 7 Deep Packet Inspection (DPI) to continuously inspect network traffic and identify malicious activities before they impact business operations. By analyzing application-layer traffic in real time, the gateway detects known threats, blocks suspicious connections, and enhances application visibility, helping organizations reduce cyber risks while maintaining reliable network communications.
 

related pd CSG 800 1


Continuous Security Monitoring with Security Logs and Scheduled Signature Updates

The PQCG-800BE provides security logs, event reports, and scheduled signature updates to simplify cybersecurity management and improve threat visibility. Administrators can monitor network activities, analyze security incidents, and identify potential threats, while scheduled threat signature updates help maintain protection against newly emerging cyber attacks with reduced management effort.
 

related pd CSG 800 2


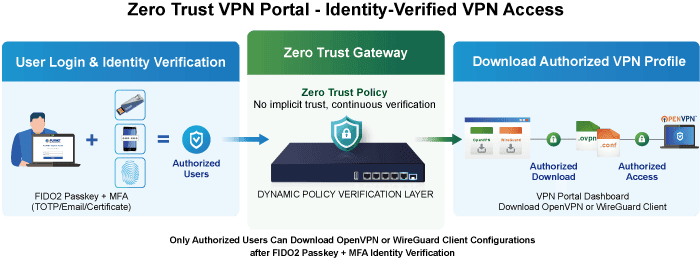
Zero Trust-Protected Access with Identity-Based Authentication

The PQCG-800BE supports Zero Trust access control, FIDO2 Passkey authentication, TOTP-based MFA, and certificate-based authentication to strengthen identity verification for enterprise resources. Built-in ZTNA enables secure application-level access, helping reduce the risks of credential compromise and unauthorized access across distributed enterprise environments.
 

ZT 800 1


التمهيد الآمن لضمان سلامة النظام الموثوقة

The PQCG-800BE incorporates نظام تثبيت آمن technology to ensure that only authenticated and trusted firmware is executed during system startup. Cryptographic image signature verification establishes a Chain of Trust across boot stages, helping protect system integrity against firmware tampering.


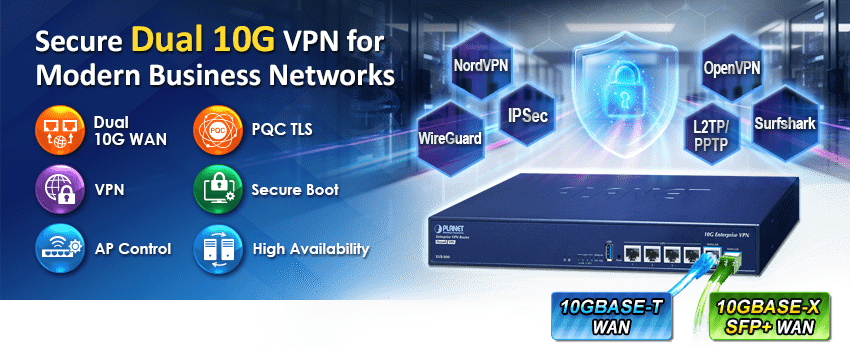
التبديل التلقائي بين شبكتي WAN

Featuring 10GBASE-T RJ45 and 10GBASE-X SFP+ WAN interfaces, the PQCG-800BE supports intelligent Dual-WAN failover to maintain Internet connectivity. When the primary WAN connection becomes unavailable, the secondary WAN interface automatically takes over, minimizing downtime for business-critical applications.


Flexible WAN Interfaces for Network Expansion

The PQCG-800BE provides flexible WAN deployment through its 10G RJ45 and 10G SFP+ interfaces, allowing administrators to choose copper or fiber connectivity according to deployment requirements. Supporting long-distance fiber transmission and high-speed Ethernet connectivity, it enables flexible network expansion for headquarters, branch offices, data centers, and industrial facilities.


Secure and Convenient Network Management

The PQCG-800BE provides HTTPS web management and SNMP management interfaces for convenient configuration and monitoring. Its built-in web interface offers an easy-to-use, platform-independent management facility, while SNMPv1, SNMPv2c, and SNMPv3 support integration with standard network management software. These management options help administrators efficiently maintain distributed network deployments.


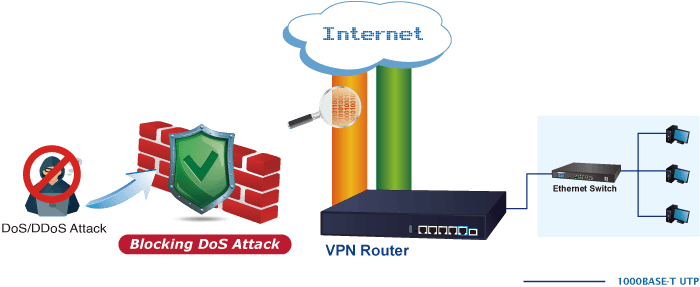
Comprehensive Firewall and Threat Defense

The PQCG-800BE integrates فحص الحزم ذي الحالة (SPI), IDS/IPS, Layer 7 DPI, and DoS/DDoS mitigation to provide comprehensive network protection. MAC and IP filtering help enforce traffic policies, while port forwarding and DMZ functions allow internal servers to provide services to Internet users according to configured access rules.
 

XVR 800 4


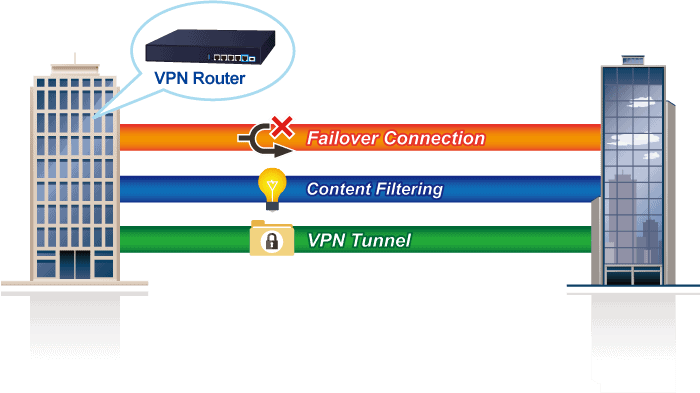
Multi-Protocol VPN Connectivity for Distributed Networks

The PQCG-800BE provides secure remote access and site-to-site connectivity through its comprehensive VPN suite. Supporting IPSe, أوبن في بي إن, شبكة سلكية, اختبار GRE, PPTP, and L2TP, it offers flexible tunneling options for branch offices, remote workers, and distributed business operations. Combined with identity-based access control, these VPN capabilities help organizations establish secure connections across public networks.
 

XVR 800 3


توجيه مرن مع إمكانية تعطيل NAT

The PQCG-800BE supports NAT disable functionality, allowing it to operate in pure routing mode for advanced network deployment scenarios. This feature is particularly beneficial for environments requiring end-to-end IP transparency, such as enterprise backbone networks, data centers, or integration with upstream security systems. By disabling NAT, administrators can achieve greater control over traffic flow and routing policies.


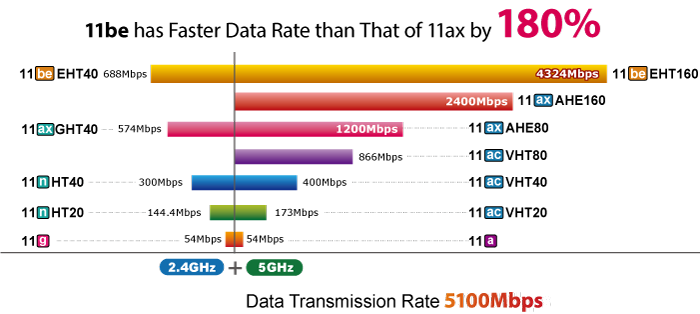
قناة فائقة الاتساع لاتصال واي فاي 7 عالي السرعة

The PQCG-800BE supports up to 160 MHz channel bandwidth and delivers a peak wireless transmission rate of up to 5100 Mbps. Designed for commercial environments, it provides the speed, efficiency, and reliable performance required for bandwidth-intensive network services.
 

WDAP C5100BE 2


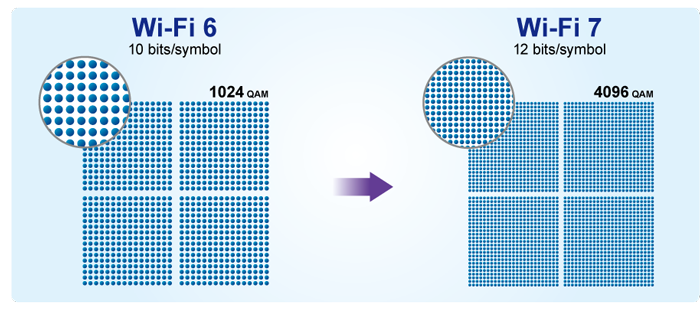
إنتاجية أعلى مع تقنية 4096-QAM

مع 4096-QAM encoding, the PQCG-800BE transmits more data within each signal, increasing wireless throughput and transmission efficiency. It is ideal for high-bandwidth applications such as 4K/8K video streaming, AR/VR experiences, and real-time cloud services.
 

WDAP C5100BE 3


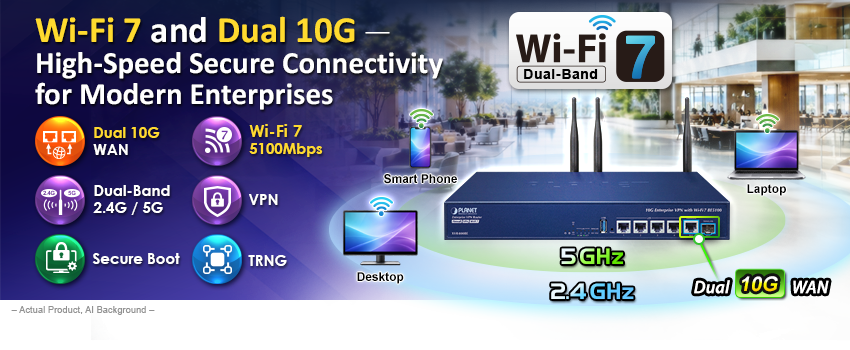
اتصال لاسلكي ثنائي النطاق موثوق

Supporting concurrent 2.4 GHz and 5 GHz wireless connectivity, the PQCG-800BE provides flexible coverage and high-speed data transmission. Its dual-band design supports reliable wireless connectivity for diverse commercial deployment requirements.
 

edm2 XVR 800BE 1


زيادة كفاءة العمل إلى أقصى حد باستخدام بوابة PLANET SD-WAN

The PQCG-800BE incorporates SD-WAN (Software-Defined Wide Area Network) functionality to optimize traffic across multiple WAN links. By managing available network connections at each site, it helps improve application performance, enhance the user experience, and simplify connectivity for distributed business operations.


Integrated Wi-Fi Management for Secure and Easy Deployment

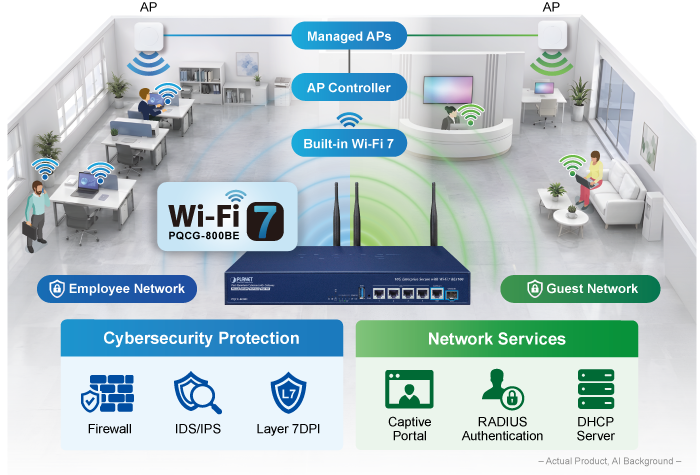
The PQCG-800BE integrates an وحدة تحكم نقاط الوصول, بوابة الوصول المقيد, مصادقة RADIUS, and DHCP server to streamline Wi-Fi deployment for small and medium-sized businesses. These built-in services reduce the need for external servers, enabling administrators to centrally manage APs, enforce access policies, and deliver secure employee and guest Wi-Fi networks with reduced setup complexity.
 

edm2 XVR 800 1


التحكم المركزي عن بعد في نقاط الوصول المُدارة

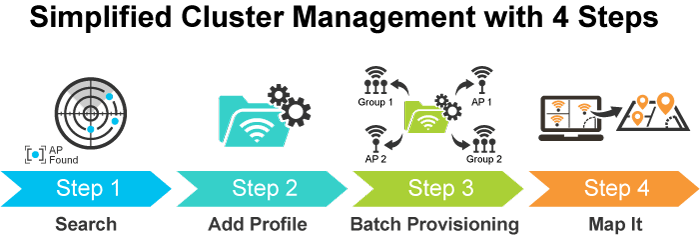
Through its intuitive web-based interface, the PQCG-800BE allows centralized control of PLANET Smart APs, with simple configuration of SSIDs, radio settings, and security policies. A quick four-step setup pushes wireless profiles to multiple APs or groups at once, enabling fast rollout and reduced deployment cost.
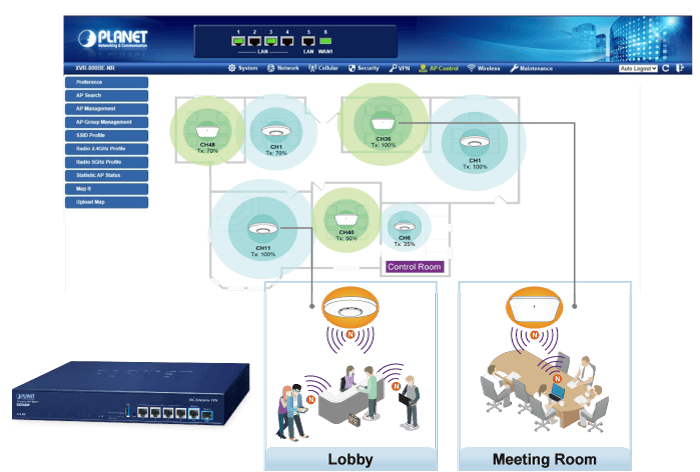
 

XVR 800 2


Administrators can cluster APs of the same model for unified management, flexibly expand or remove APs, and perform bulk provisioning or firmware upgrades from a single control point. This ensures scalable and efficient Wi-Fi management.
 

WGR 500 4PV v1.1 8


آلية تشخيص ذكية لمرض SFP

The PQCG-800BE supports جهاز مراقبة التشخيص الرقمي (SFP-DDM) functionality, allowing network administrators to monitor real-time transceiver parameters such as optical output power, optical input power, temperature, laser bias current, and supply voltage. This simplifies fiber-link monitoring and troubleshooting.


Common Intelligent SFP SFP+ Diagnosis Mechanism


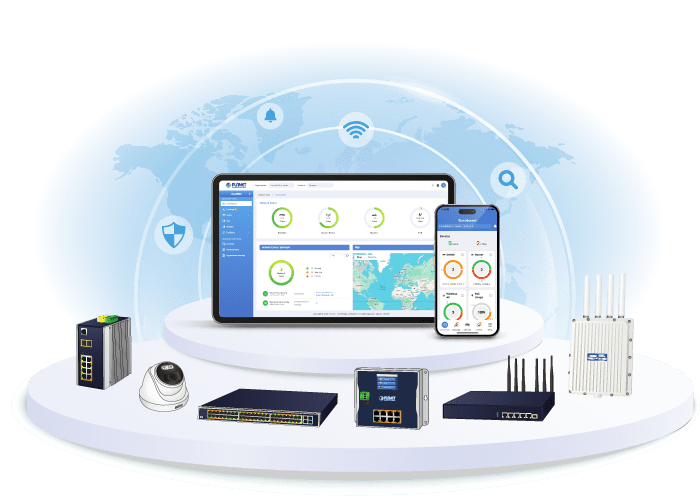
بلانيت كلاود إن إم إس – إدارة الشبكات الشاملة القائمة على السحابة

كوكب CloudNMS تُمكّن المنصة وتطبيق الهاتف المحمول موظفي تقنية المعلومات من إدارة جميع أجهزة الشبكة والأجهزة المُزوّدة بالطاقة عن بُعد في الوقت الفعلي. صُممت منصة CloudNMS خصيصًا للمؤسسات والقطاعات الصناعية، وهي تُقلل الحاجة إلى استكشاف الأخطاء وإصلاحها في الموقع من خلال توفير مراقبة مركزية، واكتشاف الأعطال، وتنبيهات فورية. 

مع CloudNMS, وبذلك، تستطيع الشركات إدارة عمليات نشر الشبكات المتنوعة بشكل أفضل. بكفاءة, بشكل آمن, وبذكاء—كل ذلك من خلال منصة واحدة قائمة على الحوسبة السحابية.
 

CloudNMS APP 5

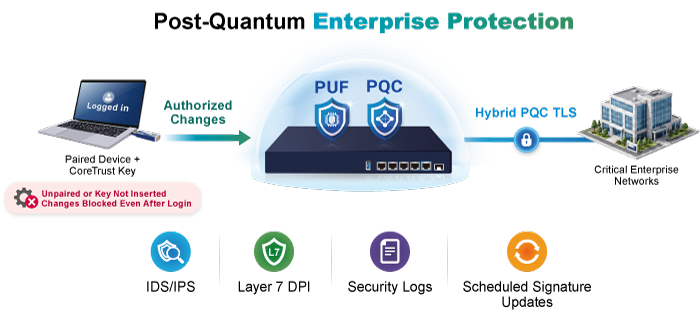
Post-Quantum Protection for Critical Enterprise Networks

ال PQCG-800BE provides secure connectivity for government agencies, financial institutions, and enterprise networks handling sensitive information. Hybrid PQC TLS supports long-term communication security, while PUF-based configuration protection allows only paired devices with an inserted CoreTrust Key to modify gateway settings. Devices that do not meet both requirements cannot change settings even after login. Integrated IDS/IPS, Layer 7 DPI, security logs, and scheduled signature updates help administrators detect threats and monitor security events across headquarters, branch offices, and remote sites.


Secure Wi-Fi 7 Connectivity with Centralized Network Management

ال PQCG-800BE combines Wi-Fi 7 5100BE dual-band connectivity with enterprise cybersecurity and centralized network management for business offices and branch networks. With a built-in وحدة تحكم نقاط الوصول, بوابة الوصول المقيد, مصادقة RADIUS, and DHCP server, administrators can centrally manage wireless APs and deploy employee and guest networks with separate access policies. Integrated IDS/IPS, Layer 7 DPI, and firewall protection help safeguard wired and wireless traffic, while dual 10G WAN interfaces, SD-WAN, and automatic failover provide reliable connectivity for cloud applications and daily business operations.


أبرز النقاط

  • PUF-based configuration protection requiring completed device pairing and an inserted CoreTrust Key
  • Hybrid Post-Quantum TLS for long-term protection against quantum-computing threats
  • Anti-SCA protection to help safeguard cryptographic keys
  • Trusted platform security with Secure Boot and PUF-assisted hardware TRNG
  • Advanced threat protection with IDS/IPS, Layer 7 DPI, content filtering and application visibility
  • Zero Trust and identity-based access with FIDO2 Passkey, TOTP MFA, certificate authentication and ZTNA
  • شبكة VPN متعددة البروتوكولات مع IPSec و OpenVPN و WireGuard و GRE و PPTP و L2TP
  • واجهات WAN مزدوجة بسرعة 10 جيجابت مع تقنية SD-WAN، وموازنة الأحمال، والتحويل التلقائي في حالة الفشل، والتوافر العالي
  • Wi-Fi 7 5100BE dual-band wireless connectivity with up to 5100Mbps
  • وحدة تحكم نقاط الوصول المتكاملة، وبوابة الوصول المقيدة، وRADIUS، ونظام إدارة الشبكة السحابية (CloudNMS)، ومراقبة الأمان


الأجهزة

  • 4 منافذ RJ45 من نوع 10/100/1000BASE-T
  • 1 1G/2.5G/5G/10GBASE-T RJ45 port for WAN/LAN interface
  • فتحة SFP+ واحدة بسرعة 1 جيجابت/2.5 جيجابت/10 جيجابت إيثرنت لواجهة WAN/LAN
  • منفذ USB واحد لعمل نسخ احتياطية واستعادة إعدادات النظام
  • Reset button
  • تركيب على سطح المكتب أو تركيب على رف


واجهة واي فاي 7 اللاسلكية

  • Supports Wi-Fi 7 (802.11be) dual-band wireless connectivity
  • Provides combined wireless speeds of up to 5100Mbps, with approximately 689Mbps at 2.4GHz and 4324Mbps at 5GHz
  • Supports up to 160MHz channel bandwidth
  • Supports 4096-QAM (4K-QAM) for increased wireless throughput
  • Advanced MIMO technology for high-performance wireless connectivity
  • Dual-band 2.4GHz and 5GHz operation for flexible wireless deployment


أمان المنصة الموثوقة

  • PUF-based configuration change authorization requiring completed device pairing and an inserted CoreTrust Key
  • Prevents configuration changes when either requirement is not met, even after connecting and logging in
  • التمهيد الآمن لضمان تشغيل البرامج الثابتة الموثوقة والمصادق عليها فقط أثناء بدء تشغيل النظام
  • PUF-assisted hardware TRNG (True Random Number Generator) for secure cryptographic key generation
  • Anti-Side-Channel Attack (Anti-SCA) protection to help safeguard cryptographic keys
  • يتبع تصميم الأمن مبادئ قانون المرونة السيبرانية للاتحاد الأوروبي (CRA).


جدار الحماية والتحكم المروري

  • جدار الحماية الخاص بفحص الحزم ذي الحالة (SPI)
  • MAC filtering and IP filtering
  • بوابات طبقة التطبيق (NAT ALGs)
  • دعم إعادة توجيه المنافذ ومنطقة DMZ


Advanced Threat Protection & Application Security

  • Intrusion Detection and Prevention (IDS/IPS)
  • Layer 7 Deep Packet Inspection (DPI)
  • Application-level traffic visibility
  • Content filtering
  • DoS/DDoS mitigation
  • SYN/ICMP flooding protection
  • Automatic and scheduled threat signature updates


Zero Trust & ZTNA

  • Zero Trust access control
  • Identity-based access policy
  • Built-in ZTNA for secure application-level access
  • Zero Trust-protected VPN access
  • Identity-based VPN authentication


Identity, Authentication & Access Services

  • FIDO2 Passkey authentication
  • TOTP-based multi-factor authentication (MFA/2FA)
  • Certificate-based authentication
  • خادم/عميل RADIUS
  • Captive Portal for controlled employee and guest access


شبكة VPN ونفق آمن

  • IPSec/خادم بعيد (من الشبكة إلى الشبكة، ومن المضيف إلى الشبكة)
  • خادم GRE، خادم PPTP
  • خادم L2TP
  • خادم/عميل SSL (OpenVPN، متوافق مع خدمات VPN مثل Surfshark و NordVPN)
  • خادم/عميل WireGuard
  • طرق التشفير: DES، 3DES، AES، AES-128/192/256
  • طرق المصادقة: MD5، SHA-1، SHA-256، SHA-384، SHA-512
  • Supports up to 100 concurrent SSL VPN connections*


التشفير والاستعداد الكمي

  • Hybrid Post-Quantum TLS key exchange using ML-KEM (Kyber) for protection against future quantum-computing threats


التوجيه، وشبكات SD-WAN، وتحسين شبكات WAN

  • المسار الثابت
  • Dynamic route
  • بروتوكول OSPF
  • تقنية SD-WAN لتحسين حركة البيانات عبر شبكات WAN المتعددة
  • موازنة الأحمال الصادرة
  • تعطيل دعم NAT لنشر وضع التوجيه النقي


التوافر العالي ومرونة الشبكة الواسعة

  • Automatic failover for dual WAN
  • التوافر العالي (HA)


خدمات الشبكة

  • عميل IP ثابت/PPPoE/DHCP لشبكة WAN
  • خادم DHCP وعميل NTP للشبكة المحلية
  • البروتوكولات: TCP/IP، UDP، ARP، IPv4، IPv6
  • جودة الخدمة، وبروتوكول إدارة مجموعات الإنترنت، وبروتوكول نقطة الاتصال الموحدة
  • استنساخ عنوان MAC
  • خدمة DDNS: PLANET DDNS، وEasy DDNS، وDynDNS، وNo-IP


إدارة الشبكات اللاسلكية ونقاط الوصول

  • وحدة تحكم مدمجة لإدارة نقاط الوصول الذكية من PLANET بشكل مركزي
  • توفير مركزي لـ SSID والراديو وسياسة الأمان
  • توفير نقاط الوصول بكميات كبيرة وترقية البرامج الثابتة


إدارة النظام ومراقبته وإعداد التقارير

  • معالج الإعداد
  • لوحة تحكم لمراقبة النظام والأمان
  • عارض سجلات الأمان وتقارير الأحداث
  • جهاز مراقبة التشخيص الرقمي (SFP-DDM)
  • إمكانية الوصول الآمن للإدارة عبر بروتوكول HTTPS؛ يدعم الوصول عبر بروتوكول HTTP
  • إدارة SNMPv1 و SNMPv2c و SNMPv3
  • إعادة التشغيل التلقائي
  • نظام إدارة الشبكة PLANET وأداة الاكتشاف الذكي لإدارة النشر
  • تطبيق PLANET CloudNMS للمراقبة في الوقت الفعلي

مواصفات الأجهزة
إيثرنت4 منافذ إيثرنت RJ45 من نوع 10/100/1000BASE-T (من المنفذ 1 إلى المنفذ 4)
1 منفذ RJ45 بسرعة 1 جيجابت/2.5 جيجابت/5 جيجابت/10 جيجابت (المنفذ 5)
يدعم وضع منفذ WAN أو وضع منفذ LAN عبر تكوين البرنامج
الفيبرمنفذ واحد من نوع SFP+ بسرعة 1 جيجابت/2.5 جيجابت/10 جيجابت إيثرنت (المنفذ 6)
يدعم وضع منفذ WAN أو وضع منفذ LAN عبر تكوين البرنامج
منفذ USBمنفذ USB 2.0 واحد لعمل نسخ احتياطية واستعادة إعدادات النظام
زر إعادة الضبطإعادة ضبط المصنع الافتراضي
مروحة حرارية1
مؤشرات LEDنظام:
 PWR, Internet, (أخضر)
Wireless Interfaces (2.4G & 5G)
LNK/ACT (أخضر)
واجهات إيثرنت (المنافذ من 1 إلى 4):
10/100/1000 LNK/ACT (أخضر)
واجهات إيثرنت (المنفذ 5):
1G/2.5G/5G/10G LNK/ACT (أخضر)
واجهات الألياف (المنفذ 6):
1G/2.5G/10G LNK/ACT (أخضر)
تثبيتتركيب على سطح المكتب أو تركيب على رف
متطلبات الطاقة100-240 فولت تيار متردد، 50/60 هرتز، استشعار تلقائي
استهلاك الطاقة / تبديدهاMax. 3.3 watts/10.92BTU (Power on without any connection)
Max. 11 watts/37.53BTU (Full loading)
وزن1725 غرام
الأبعاد (العرض × العمق × الارتفاع)330.2 × 200 × 43.1 مم، ارتفاع وحدة واحدة
حاويةمعدن
مواصفات الاتصال اللاسلكي
معيار لاسلكيIEEE 802.11be (Wi-Fi 7)
نطاق التردد2.4 جيجاهرتز و 5 جيجاهرتز
معدل نقل البيانات اللاسلكيةسرعة تصل إلى 5100 ميجابت في الثانية
معدل نقل البيانات 2.4 جيجاهرتزتصل السرعة إلى حوالي 689 ميجابت في الثانية
معدل نقل البيانات 5 جيجاهرتزتصل إلى حوالي 4324 ميجابت في الثانية
عرض القناةيصل إلى 160 ميجاهرتز
تعديل4096-QAM (4K-QAM)
MIMOتقنية MIMO المتقدمة
خدمات الأمن
Hardware Root of TrustPUF-based hardware protection for configuration change authorization
Configuration Change AuthorizationRequires completed device pairing and an inserted CoreTrust Key to modify gateway settings.
Devices without either requirement cannot change settings, even after connecting and logging in.
Side-Channel Attack ProtectionAnti-SCA protection to help safeguard cryptographic keys against side-channel attacks
Hardware Random Number GeneratorPUF-assisted hardware TRNG for secure cryptographic key generation
أمان جدار الحمايةHardware TRNG for secure cryptographic key generation
فحص الحزم ذي الحالة (SPI)
Security log and event reporting
Automatic threat signature updates
يحجب هجمات حجب الخدمة/هجمات حجب الخدمة الموزعة
Role-based access policy enforcement
ALG (بوابة طبقة التطبيق)SIP، RTSP، FTP، H.323، TFTP
NATنقل البضائع
مضيف منطقة منزوعة السلاح
UPnP
تعطيل NAT (يدعم وضع التوجيه)
تصفية المحتوىتصفية عناوين MAC
تصفية عناوين IP
تصفية الويب
إدارة عرض النطاق التردديموازنة الأحمال الصادرة
تجاوز الأعطال لشبكة WAN المزدوجة
جودة الخدمة (QoS)
Zero TrustZero Trust access control with identity verification
Multi-factor authentication via external hardware security key support
Intrusion Prevention SystemIntrusion Detection and Prevention (IDS/IPS)
Layer 7 Deep Packet Inspection (DPI)
Application-level traffic visibility
نظام تثبيت آمنEstablishes a Chain of Trust (CoT) across all boot stages via cryptographic image signature verification
التواصل
وضع التشغيلوضع التوجيه
بروتوكول التوجيهالمسار الثابت، المسار الديناميكي (RIP)، بروتوكول OSPF
شبكة VLAN802.1Q Tag-based, Port-based, Multi-VLAN
البث المتعددوكيل IGMP
معدل نقل البيانات عبر NATMax. 9.4Gbps
موازنة الأحمال الصادرةالخوارزميات المدعومة: الوزن
بروتوكولIPv4، IPv6، TCP/IP، UDP، ARP، HTTP، HTTPS، NTP، DNS، PLANET DDNS، PLANET Easy DDNS، DHCP، PPPoE، SNMPv1/v2c/v3
الميزات الرئيسيةHA (التوافر العالي)
بوابة الوصول المقيد
خادم/عميل RADIUS
التحكم في نقاط الوصول
VPN
وظيفة VPNIPSec (Net-to-Net, Host-to-Net)
IPSec Remote Server
اختبار GRE
خادم PPTP
خادم L2TP
SSL Server
SSL Client (Open VPN, Surfshark, NordVPN, PureVPN)
WireGuard VPN Server/Client
سعة نفق VPN حسب البروتوكولIPSec: 16
GRE: 5
PPT: 100
SSL VPN: 200
معدل نقل بيانات VPNL2TP (1Gbps): 145~463Mbps
L2TP (10Gbps): 483~885Mbps
L2TP/IPsec (1Gbps): 150~334Mbps
L2TP/IPsec (10Gbps): 438~496Mbps
IPsec/AES128 (1Gbps): 894~910Mbps
IPsec/AES128 (10Gbps): 1,110~1,310Mbps
IPsec/AES256 (1Gbps): 752~842Mbps
IPsec/AES256 (10Gbps): 864~1,060Mbps
WireGuard (1Gbps): 815~883Mbps
WireGuard (10Gbps): 1,430~1,890Mbps
أساليب التشفيرتشفير DES أو 3DES أو AES أو AES-128/192/256
بروتوكول PQC TLS (بروتوكول أمان طبقة النقل بعد التشفير الكمي) جاهز
Supports Hybrid Post-Quantum TLS key exchange using ML-KEM (Kyber)
أساليب المصادقةSHA-256/SHA-384/SHA-512 authentication algorithm
TLS_KYBER_RSA_WITH_AES_256_GCM_SHA384
FIDO2 Passkey authentication
Certificate-based authentication
TOTP MFA
مصادقة RADIUS
إدارة
واجهات الإدارة الأساسيةمتصفح الويب
SNMP الإصدار 1، الإصدار 2c
أداة PLANET Smart Discovery / UNI-NMS مدعومة
PLANET NMS System/CloudNMS
واجهات إدارة آمنةSSHv2، TLSv1.3، SNMP v3
سجل النظامسجل أحداث النظام
Security Log
Event Report
Scheduled Signature Update
آحرونمعالج الإعداد
لوحة التحكم
حالة النظام/الخدمة
إحصائيات
Security Monitoring Dashboard
حالة الاتصال
إعادة التشغيل التلقائي
التشخيص
الامتثال للمعايير
الامتثال التنظيميCE، FCC
مواصفات البيئة
التشغيلدرجة الحرارة: من 0 إلى 50 درجة مئوية
الرطوبة النسبية: 5 ~ 95% (بدون تكثف)
تخزيندرجة الحرارة: من -10 إلى 60 درجة مئوية
الرطوبة النسبية: 5 ~ 95% (بدون تكثف)

معلومات الطلب

PQCG-800BE

بوابة أمن سيبراني مزدوجة مقاومة للحوسبة الكمومية، تدعم تقنية PUF بسرعة 10 جيجابت/ثانية، مزودة بتقنية Wi-Fi 7 5100BE

✉

انضم إلى قائمتنا البريدية

احصل على آخر الأخبار والعروض والتحديثات من شركة بلانيت تكنولوجي مباشرة إلى بريدك الإلكتروني.

نحن نحترم خصوصيتك. يمكنك إلغاء الاشتراك في أي وقت.

اشترك في النشرة الإخبارية الإلكترونية لـ PLANET

احصل على أحدث معلومات المنتجات وأخبار الشركة!